Limit Per User
Override the session cap for a single account.
- Per-user concurrent-session override on the profile screen
- Takes precedence over both global and per-role limits
- Blank or zero simply falls back to the global limit
- Your chosen login logic still applies — only the number changes
- Enforced on the next login, with nonce and capability checks
- Works with the free Loggedin core plugin
- Automatic updates & support while licensed
- 1, 5 or 10-site licenses
- 7-day money-back guarantee
- Documentation docs.foxelabs.com (opens in new tab)
- Loggedin core plugin Free · required
- Get support Straight to the team
Requires the free Loggedin plugin to be installed and active.
About Limit Per User
Give one account more (or fewer) concurrent sessions than your global limit, straight from the user's profile screen.
What it does
Some accounts legitimately need a different cap than everyone else — a shared editorial login, a service account, a support desk with three people on rotation, or an executive roaming between four devices. Tuning the global limit to suit them loosens it for the entire site.
Limit Per User sets a concurrent-session limit on one account, leaving everyone else exactly as they were.
No extra settings screen
There’s no panel to hunt for. The control is a single number field on the WordPress profile screen — your own profile, and the edit-user screen admins see — under a Loggedin heading near the bottom of the page.
Leave it blank to use whatever limit already applies. Enter a number to cap that one account. It saves with the profile itself, via the normal Update Profile button.
How the number is read
| Value | What happens |
|---|---|
| Blank | No override — global or role limit applies |
0 or negative | Same as blank; the stored value is removed |
1 or more | That account is capped at this many sessions |
Zero would be indistinguishable from “no override” anyway, so the add-on
deletes the row rather than leaving dead data in usermeta.
Priority
When several limit add-ons are active, per-user always wins:
per-user → per-role → global.
An account with a per-user override uses that value regardless of any role limit. Only the number changes — your chosen login logic (block the new login, log out the oldest, or log out all) still governs what happens when the cap is reached.
Safe to hand out
The change takes effect on the account’s next login attempt, and saves are
protected by a nonce and the edit_user capability, so nobody can raise
their own limit through a crafted request.
Managing caps for whole groups rather than individuals? Use Limit Per Role for the bulk of your site and keep this add-on for the handful of accounts that are genuine exceptions.
Limit Per User in the WordPress admin
Every screen Limit Per User adds, and where to find it.
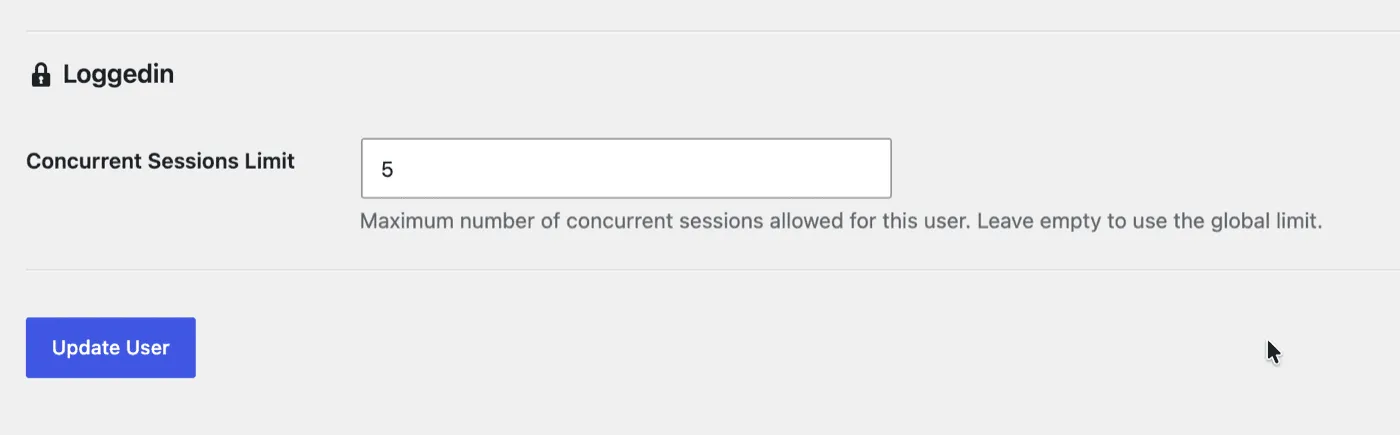
No settings screen at all
The override lives on the profile screen an admin is already editing, under a Loggedin heading near the bottom of the page.
Blank means "use the global limit" — and so does zero, which removes the stored value entirely.
Frequently asked questions
How do I limit concurrent logins for one WordPress user?
Install the free Loggedin plugin with the Limit Per User add-on, edit the account under Users → All Users, and enter a number in the Concurrent Sessions Limit field. That account is capped at that number regardless of your global setting.
Where is the per-user login limit field?
On the WordPress profile screen — both your own profile and the edit-user screen administrators see. It sits near the bottom under a Loggedin heading. There is no separate settings panel for this add-on.
What happens if I leave the per-user limit blank?
The account falls back to your global limit, or to its role limit if you also run Limit Per Role. Entering zero behaves the same way, and the add-on deletes the stored value rather than keeping a meaningless row.
Which limit wins when several Loggedin add-ons are active?
Per-user beats per-role, and per-role beats the global setting. An account with a per-user override always uses that number, whatever limits are configured for the roles it holds.
When does a changed per-user limit take effect?
On that user's next login attempt. Changing the number does not sign out sessions that already exist — it changes what happens the next time the account tries to sign in.
Can a non-admin raise their own session limit?
No. Saving the field requires the edit_user capability and passes a nonce check, so an ordinary user cannot lift their own cap by crafting a request against their profile.
Learn how we can help you build better.
Questions about a plugin, a licence, or an expert advisor — ask and get a straight answer from the team that wrote the code.